VMware Cloud on AWS – TMCHAM – Part 16 – Remove External Datastores

In this edition of Things My Customers Have Asked Me (TMCHAM), I’m going to do a (really) short post on removing external datastores on the VMware-managed VMware Cloud on AWS platform. It might seem like a simple thing, but it can be confusing for customers who haven’t done it before.


The Problem

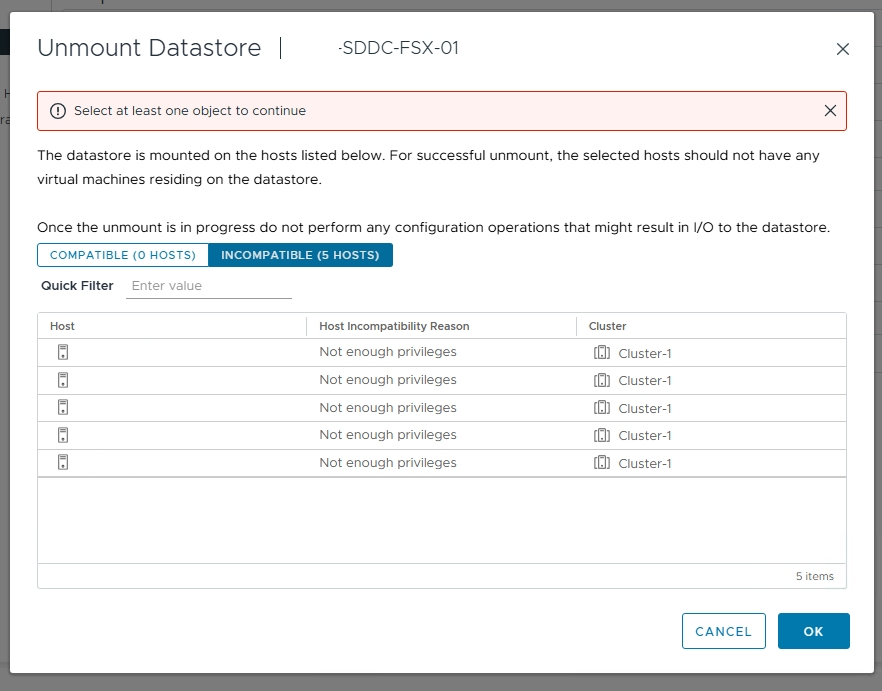
If you’ve used an external datastore (either FSx for NetApp ONTAP or the artist formerly known as VMware Cloud Flex Storage) with your SDDC, you’ll know that management of the connection of the datastores to your SDDC is done via the Cloud Console, and not via vCenter. There might come a time when you want to remove that storage, either because you’ve bought more nodes and want to use vSAN, or you’re possibly shrinking your footprint. Whatever the reason, if you do try to remove the datastore via vCenter (assuming you’ve removed your workloads from the datastore), you’ll get an error about insufficient privileges. At first it might seem like it’s because you have VMs still present on the datastore (and if this is the case, contact Global Support to help you if you can’t find them). It’s more likely, however, that you’re not in the right place to do this activity.


The Solution

The solution is simple. In the VMware Cloud Console, go to the Storage tab of the SDDC you want to remove the datastore from, and click on Detach Datastore. And that’s it. It won’t work if you’ve got workloads running there, so make sure you’ve cleaned everything up / moved it somewhere else before you attempt this one.

VMware Cloud on AWS – What’s New – December 2025

I posted last month about what’s new in VMware Cloud on AWS, particularly as it related to stretched cluster and HCX enhancements. The team has been working hard on some more new features, and I thought I’d cover them off briefly here. More detail can be found in the VMware Cloud on AWS Release Notes are here, and there’s a great blog post from the team here.


What’s New?

New Host Usage Report API

Have you been wondering what’s going on with resources in your VMC on AWS environment? Wonder no more. All the cool cloud kids are using APIs, and VMC on AWS is no different. Now you can retrieve daily host usage reports for any date range and filter by region, instance type, SKU, and other attributes – all via the API. There’s no need to call me and ask for a report on what’s happening, nor do you need to log a ticket to get access to the information. Here’s what a sample query looks like.

curl -H 'Authorization: <value>' https://{api_host}/api/activityanalytic/{org_id}/hosts/{freq}/usage-report?start_date=value&end_date=v

Check out the documentation here.

Redesigned VMware Cloud on AWS UI

The VMware Cloud on AWS UI has also had a facelift, and the interface is more streamlined and easier to navigate. You can access it at https://vmc.broadcom.com.

VMC Sizer & Cluster Conversion Updates

Ever since I started working with VMware Cloud on AWS, I’ve been a huge fan of the VMC Sizer tool. It’s so much better than trying to build solution estimates with a spreadsheet and a dream. If you’re an existing I3.metal customer, you’ve likely (hopefully) been planning a migration to I3en.metal or I4i.metal nodes. The conversion estimates can be a bit of a mystery, and have frequently required involving people like me and folks from the SRE team to provide these estimates. The product team has been working to make the process more streamlined, while giving customers improved visibility into why the numbers are the way they are. The output from sizing estimates now provides clear reasoning behind why a specific number of hosts is required, and this is based on 6 elements (compute, memory, storage utilisation (with both conservative and aggressive options), vSAN storage policies, and NSX Edges). It’s never been a simple matter of saying two I3.metal hosts equals one I4i.metal host, and now the sizer output reflects this more clearly.

The following constraints should be noted:

  • Final host counts and sizing will be validated during the actual cluster conversion. Sometimes you end up with more, sometimes you end up with fewer hosts.
  • Customers should re-run sizing evaluations after any significant configuration, resource, or other changes. Please don’t add another 30TiB workload to your cluster and expect the same result.
  • No RAID policy changes are made during conversion. This is especially notable if you’re using custom storage policies in your environment.
  • Subscription estimates provided as part of this workflow are for planning purposes only and do not represent guaranteed final requirements.
  • Actual subscription needs may be higher than estimated, requiring additional subscription purchase post-conversion. You’re given a small window to make good on this.
  • Refunds or subscription reductions will not be provided if estimates exceed actual needs.


Thoughts

As I mentioned in my previous post, VMware Cloud on AWS is not going anywhere, and the product and engineering teams continue to innovate and work hard to ensure that users get the best value from their investment in the VMware Cloud on AWS solution. The Host Usage Report is extremely useful, and for those customers concerned about cluster conversions, the improvements to the VMC Sizer should improve the confidence in the sizing process.

Brisbane VMUG – November 2025

The November edition of the Brisbane VMUG meeting will be held on Thursday 27th November at Christie Spaces, 320 Adelaide St (Room F) from 3pm – 5pm. It’s sponsored by Broadcom and Google Cloud and promises to be a great afternoon.

  • Session 1: Modernize All the Things with VKS in VMware Cloud Foundation (Presenter: Mike Francis – Principal Transformation Architect – Broadcom). VCF Supervisor and Supervisor Services is a pivotal change. In this session we will discuss what Supervisor is, how you should view Supervisor Services as the foundation for your cloud and how this capability modernises on-premise Cloud Operations. We will demonstrate Supervisor and Supervisor Services and draw the connection between it and operations modernisation.
  • Session 2: What’s new with GCVE and native cloud integration (Presenter: Clay Quinn – Senior Solution Architect – Google Cloud). We will explore the seamless architecture between private SDDC and Google’s cloud-native ecosystem, demonstrating how high-bandwidth, low-latency networking enables direct access to services like BigQuery, Cloud Storage, and Vertex AI. Discussion of practical use cases for extending your existing VMware estate, allowing modernization of applications, unification of operations, and leveraging advanced analytics without the risk or complexity of immediate refactoring.

Broadcom and Google Cloud have gone to great lengths to make sure this will be a fun and informative session. You can find out more information and register for the event here.

Random Short Take #103

Random short take #103. Want news? You’re probably not in the right place. Let’s get random.

Random Short Take #102

Random short take #102. You’ll see from the age of some of these stories that this one has been in drafts for far too long.

NetApp Cloud Storage Announcements – February 2025


NetApp recently made some announcements around its cloud storage capabilities as part of a larger series of product announcements. I thought I’d share some notes and some brief thoughts here.


Azure NetApp Files

New capability – Cost optimisation

New capability – Resilience

There’s also preview support for backing up large volumes and performing single file restores from backup.


Amazon FSx for NetApp ONTAP

There’s a new AWS CloudFormation package Amazon FSx for NetApp ONTAP that unlocks advanced ONTAP operations, including:

  • SnapMirror creation (including ClusterPeer and SVM Peer);
  • iSCSI (LUN and iGroup) creation;
  • CIFS Share creation;
  • Snapshot and Snapshot Policy creation; and
  • Advanced Volume creation.

[image courtesy of NetApp]


Thoughts

Why am I writing about FSx for NetApp ONTAP on my weblog? And why should you be interested in a few minor enhancements to this and to Azure NetApp Files? How do these technologies even make sense when the benefits of public cloud are right there? Why would organisations not just use the hyperscaler-native storage solutions available to them? It’s for the same reason that numerous organisations have adopted VMware Cloud on AWS and Azure VMware Solution, sometimes your applications need something different to what the public cloud can offer, at least until those applications have undergone some kind of transformation. I have plenty of customers in my day job taking advantage of FSx for NetApp ONTAP with their VMware Cloud on AWS deployments because the linear scalability of hyper-converged infrastructure has proven problematic for storage-heavy workloads. Additionally, they get the benefit of being able to leverage the NetApp tools they know and love, just in a cloud context. It’s great to see NetApp continue to add features and functionality to both Azure NetApp Files and FSx for NetApp ONTAP. If you’re struggling with shifting storage-dense workloads to public cloud while needing to stay within the confines of a VMware-based solution, these offerings can really help the economics make sense, even for enterprises, not just the t-shirt and jeans cloud-native types.

Random Short Take #85

Welcome to Random Short Take #85. Let’s get random.

VMware Cloud on AWS – Supplemental Storage – A Few Notes …

At VMware Explore 2022 in the US, VMware announced a number of new offerings for VMware Cloud on AWS, including something we’re calling “Supplemental Storage”. There are some great (official) posts that have already been published, so I won’t go through everything here. I thought it would be useful to provide some high-level details and cover some of the caveats that punters should be aware of.


The Problem

VMware Cloud on AWS has been around for just over 5 years now, and in that time it’s proven to be a popular platform for a variety of workloads, industry verticals, and organisations of all different sizes. However, one of the challenges that a hyper-converged architecture presents is that resource growth is generally linear (depending on the types of nodes you have available). In the case of VMware Cloud on AWS, we (now) have 3 node types available for use: the I3, I3en, and I4i. Each of these instances provides a fixed amount of CPU, RAM, and vSAN storage for use within your VMC cluster. So when your storage grows past a certain threshold (80%), you need to add an additional node. This is a longwinded way of saying that, even if you don’t need the additional CPU and RAM, you need to add it anyway. To address this challenge, VMware now offers what’s called “Supplemental Storage” for VMware Cloud on AWS. This is ostensibly external datastores presented to the VMC hosts over NFS. This comes in two flavours: FSx for NetApp ONTAP and VMware Cloud Flex Storage. I’ll cover this in a little more detail below.

[image courtesy of VMware]


Amazon FSx for NetApp ONTAP

The first cab off the rank is Amazon FSx for NetApp ONTAP (or FSxN to its friends). This one is ONTAP-like storage made available to your VMC environment as a native service. It’s fully customer managed, and VMware managed from a networking perspective.

[image courtesy of VMware]

There’s a 99.99% Availability SLA attached to the service. It’s based on NetApp ONTAP, and offers support for:

  • Multi-Tenancy
  • SnapMirror
  • FlexClone
​Note that it currently requires VMware Managed Transit Gateway (vTGW) for Multi-AZ deployment (the only deployment architecture currently supported), and can connect to multiple clusters and SDDCs for scale. You’ll need to be on SDDC version 1.20 (or greater) to leverage this service in your SDDC, and there is currently no support for attachment to stretched clusters. While you can only connect datastores to VMC hosts using NFSv3, there is support for connecting directly to guest VMs via other protocols. More information can be found in the FAQ here. There’s also a simulator you can access here that runs you through the onboarding process.


VMware Cloud Flex Storage

The other option for supplemental storage is VMware Cloud Flex Storage (sometimes referred to as VMC-FS). This is a datastore presented to your hosts over NFSv3.

Overview

VMware Cloud Flex Storage is:

  • A natively integrated cloud storage service for VMware Cloud on AWS that is fully managed by VMware;
  • Cost effective multi-cloud storage solution built on SCFS;
  • Delivered via a two-tier architecture for elasticity and performance (AWS S3 and local NVMe cache); and
  • Provides integrated Data-Management.

In short, VMware has taken a lot of the technology used in VMware Cloud Disaster Recovery (the result of the Datrium acquisition in 2020) and used it to deliver up to 400 TiB of storage per SDDC.

[image courtesy of VMware]
The intent of the solution, at this stage at least, is that it is only offered as a datastore for hosts via NFSv3, rather than other protocols directly to guests. There are some limitations around the supported topologies too, with stretched clusters not being currently supported. From a disaster recovery perspective, it’s important to note that VMware Cloud Flex Storage is currently only offered on a single-AZ basis (although the supporting components are spread across multiple Availability Zones), and there is also no support for VMware Cloud Disaster Recovery co-existence with this solution.


Thoughts
I’ve only been at VMware for a short period of time, but I’ve had numerous conversations with existing and potential VMware Cloud on AWS customers looking to solve their storage problems without necessarily putting everything on vSAN. There are plenty of reasons why you wouldn’t want to use vSAN for high capacity storage workloads, and I believe these two initial solutions go some ways to solving that issue. Many of the caveats that are wrapped around these two products at General Availability will be removed over time, and the traditional objections relating to VMware Cloud on AWS being not great at high-capacity, cost-effective storage will also have been removed.
Finally, if you’re an existing NetApp ONTAP customer, and were thinking about what you were going to do with that Petabyte of unstructured data you had lying about when you moved to VMware Cloud on AWS, or wanting to take advantage of the sweat equity you’ve poured into managing your ONTAP environment over the years, I think we’ve got you covered as well.

VMware Cloud on AWS – TMCHAM – Part 3 – SDDC Lifecycle

In this episode of Things My Customers Have Asked Me (TMCHAM), I’m going to delve into some questions around the lifecycle of the VMware-managed VMware Cloud on AWS platform, and what customers need to know to make sense of it all.


The SDDC

If you talk to VMware folks about VMware Cloud on AWS, you’ll hear a lot of talk about software-defined data centres (SDDCs). This is the logical construct in place that you use within your Organization to manage your hosts and clusters, in much the same fashion as you would your on-premises workloads. Unlike most on-premises workloads, however, the feeding and watering of the SDDC, from a software currency perspective, is done by VMware.

Release Notes

If you’ve read the VMware Cloud on AWS Release Notes, you’ll see something like this at the start:

“Beginning with the SDDC version 1.11 release, odd-numbered releases of the SDDC software are optional and available for new SDDC deployments only. By default, all new SDDC deployments and upgrades will use the most recent even-numbered release. If you want to deploy an SDDC with an odd-numbered release version, contact your VMware TAM, sales, or customer success representative to make the request.”

Updated on: 5 April  2022

Essential Release: VMware Cloud on AWS (SDDC Version 1.18) | 5 April 2022

Optional Release: VMware Cloud on AWS (SDDC Version 1.17) | 19 November 2021

Basically, when you deploy onto the platform, you’ll usually get put on what VMware calls an “Essential” release. From time to time, customers may have requirements that mean that they qualify to be deployed on an “Optional” release. This might be because they have a software integration requirement that hasn’t been handled in 1.16, for example, but is available for 1.17. It’s also important to note that each major release will have a variety of minor releases as well, depending on issues that need to be resolved or features that need to be rolled out. So you’ll also see references to 1.16v5 in places, for example.

Upgrades and Maintenance

So what happens when your SDDC is going to be upgraded? Well, we let you know in advance, and it’s done in phases, as you’d imagine.
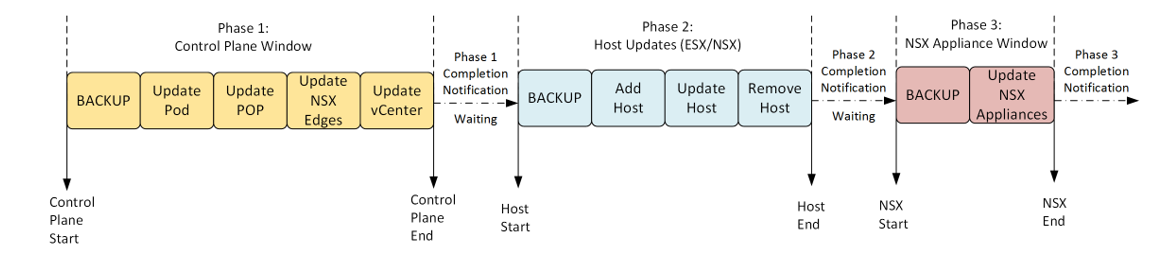
[image courtesy of VMware]

You can read more about the process here, and there’s a blog post that covers the release cadence here. VMware also does the rollout of releases in waves, so not every customer has the upgrade done at the same time. If you’re the type of customer that needs to be on the latest version of everything, or perhaps you have a real requirement to be near the front of the line, you should talk to your account team and they’ll liaise with the folks who can make it happen for you. When the upgrades are happening, you should be careful not to:

  • Perform hot or cold workload migrations. Migrations fail if they are started or in progress during maintenance.
  • Perform workload provisioning (New/Clone VM). Provisioning operations fail if they are started or in progress during maintenance.
  • Make changes to Storage-based Policy Management settings for workload VMs.

You should also ensure that there is enough storage capacity (> 30% slack space) in each cluster.

How Long Will It Take?

As usual, it depends. But you can make some (very) rough estimates by following the guidance on this page.

Will My SDDC Expire?

Yes, your SDDC version will some day expire. But it will be upgraded before that happens. There’s a page where you can look up the expiration dates of the various SDDC releases. It’s all part of the lifecycle part of the SDDC lifecycle.

Correlating VMware Cloud on AWS with Component Releases

Ever found yourself wondering what component versions are being used in VMware Cloud on AWS? Wonder no more with this very handy reference.


Conclusion

There’s obviously a lot more that goes on behind the scenes to keep everything running in tip-top shape for our customers. All of this talk of phases, waves, and release notes can be a little confusing if you’re new to the platform. Having worked in a variety of (managed and unmanaged) service providers over the years, I do like that VMware has bundled up all of this information and put it out there for people to check out. As always, if you’ve got questions about how the various software integrations work, and you can’t find the information in the documentation, reach out to your local account team and they’ll be able to help.

VMware Cloud on AWS – TMCHAM – Part 2 – VCDR Notes

In this episode of “Things My Customers Have Asked Me” (or TMCHAM for short), I’m going to dive into a few questions around VMware Cloud Disaster Recovery (VCDR), a service we offer as an add-on to VMware Cloud on AWS. If you’re unfamiliar with VCDR, you can read a bit more about it here.

VCDR Roles and Permissions

Can RBAC roles be customised? Not really, as these are cascaded down from the Cloud Services hub. As I understand it, I don’t believe you have granular control over it, just the pre-defined, default roles as outlined here, so you need to be careful about what you hand out to folks in your organisation. To see what Service Roles have been assigned to your account, in the VMware Cloud Services, go to My Account, and then click on My Roles. Under Service Roles, you’ll see a list of services, such as VCDR, Skyline, and so on. You can then check what roles have been assigned. 

VCDR Protection Groups

VCDR Protection Groups are the way that we logically group together workloads to be protected with the same RPO, schedule, and retention. There are two types of protection group: standard-frequency and high-frequency. Standard-frequency snapshots can be run as often as every 4 hours, while high-frequency snapshots can go as often as every 30 minutes. You can read more on protection groups here. It’s important to note that there are some caveats to be aware of with high-frequency snapshots. These are outlined here.

30-minute RPOs were introduced in late 2021, but there are some caveats that you need to be aware of. Some of these are straightforward, such as the minimum software levels for on-premises protection. But you also need to be mindful that VMs with existing vSphere snapshots will not be included, and, more importantly, high-frequency snapshots can’t be quiesced.

Can you have a VM instance in both a standard- and high-frequency snapshot protection group?  Would this allow us to get the best of both worlds – e.g. RPO could be as low as 30 minutes, but with a guaranteed snapshot of 4 hours?  Once you do a high-frequency snap on a VM, it keeps using that mechanism thereafter, even if it sits in a protection group using standard protection. Note also that you set a schedule for a protection group, so you can have snapshots running ever 30 mins and kept for a particular period of time (customer selects this). You could also run snapshots at 4 hours and keep those for a period of time too. While you can technically have a VM in multiple groups, what you’re better off doing is configuring a variety of schedules for your protection groups to meet those different RPOs.

Quiesced Snapshots

What happens to a VM during a quiesced state – would we experience micro service outages? The best answer I can give is “it depends”. The process for the standard, quiesced snapshot is similar to the one described here. The VM will be stunned by the process, so depending on what kind of activity is happening on the VM, there may be a micro outage to the service.

Other Considerations

The documentation talks about not changing anything when a scheduled snapshot is being run – how do we manage configuration of the SDDC if jobs are running 24/7?  Seems odd that nothing can be changed when a scheduled snapshot is being run? This refers more to the VM that is being snapped. i.e. Don’t change configs or make changes to the environment, as that would impact this VM. It’s not a blanket rule for the whole environment. 

Like most things, success with VCDR relies heavily on understanding the outcomes your organisation wants to achieve, and then working backwards from there. It’s also important to understand that this is a great way to do DR, but not necessarily a great way to do standard backup and recovery activities. Hopefully this article helps clarify some of the questions folks have around VCDR, and if it doesn’t, please don’t hesitate to get in contact.